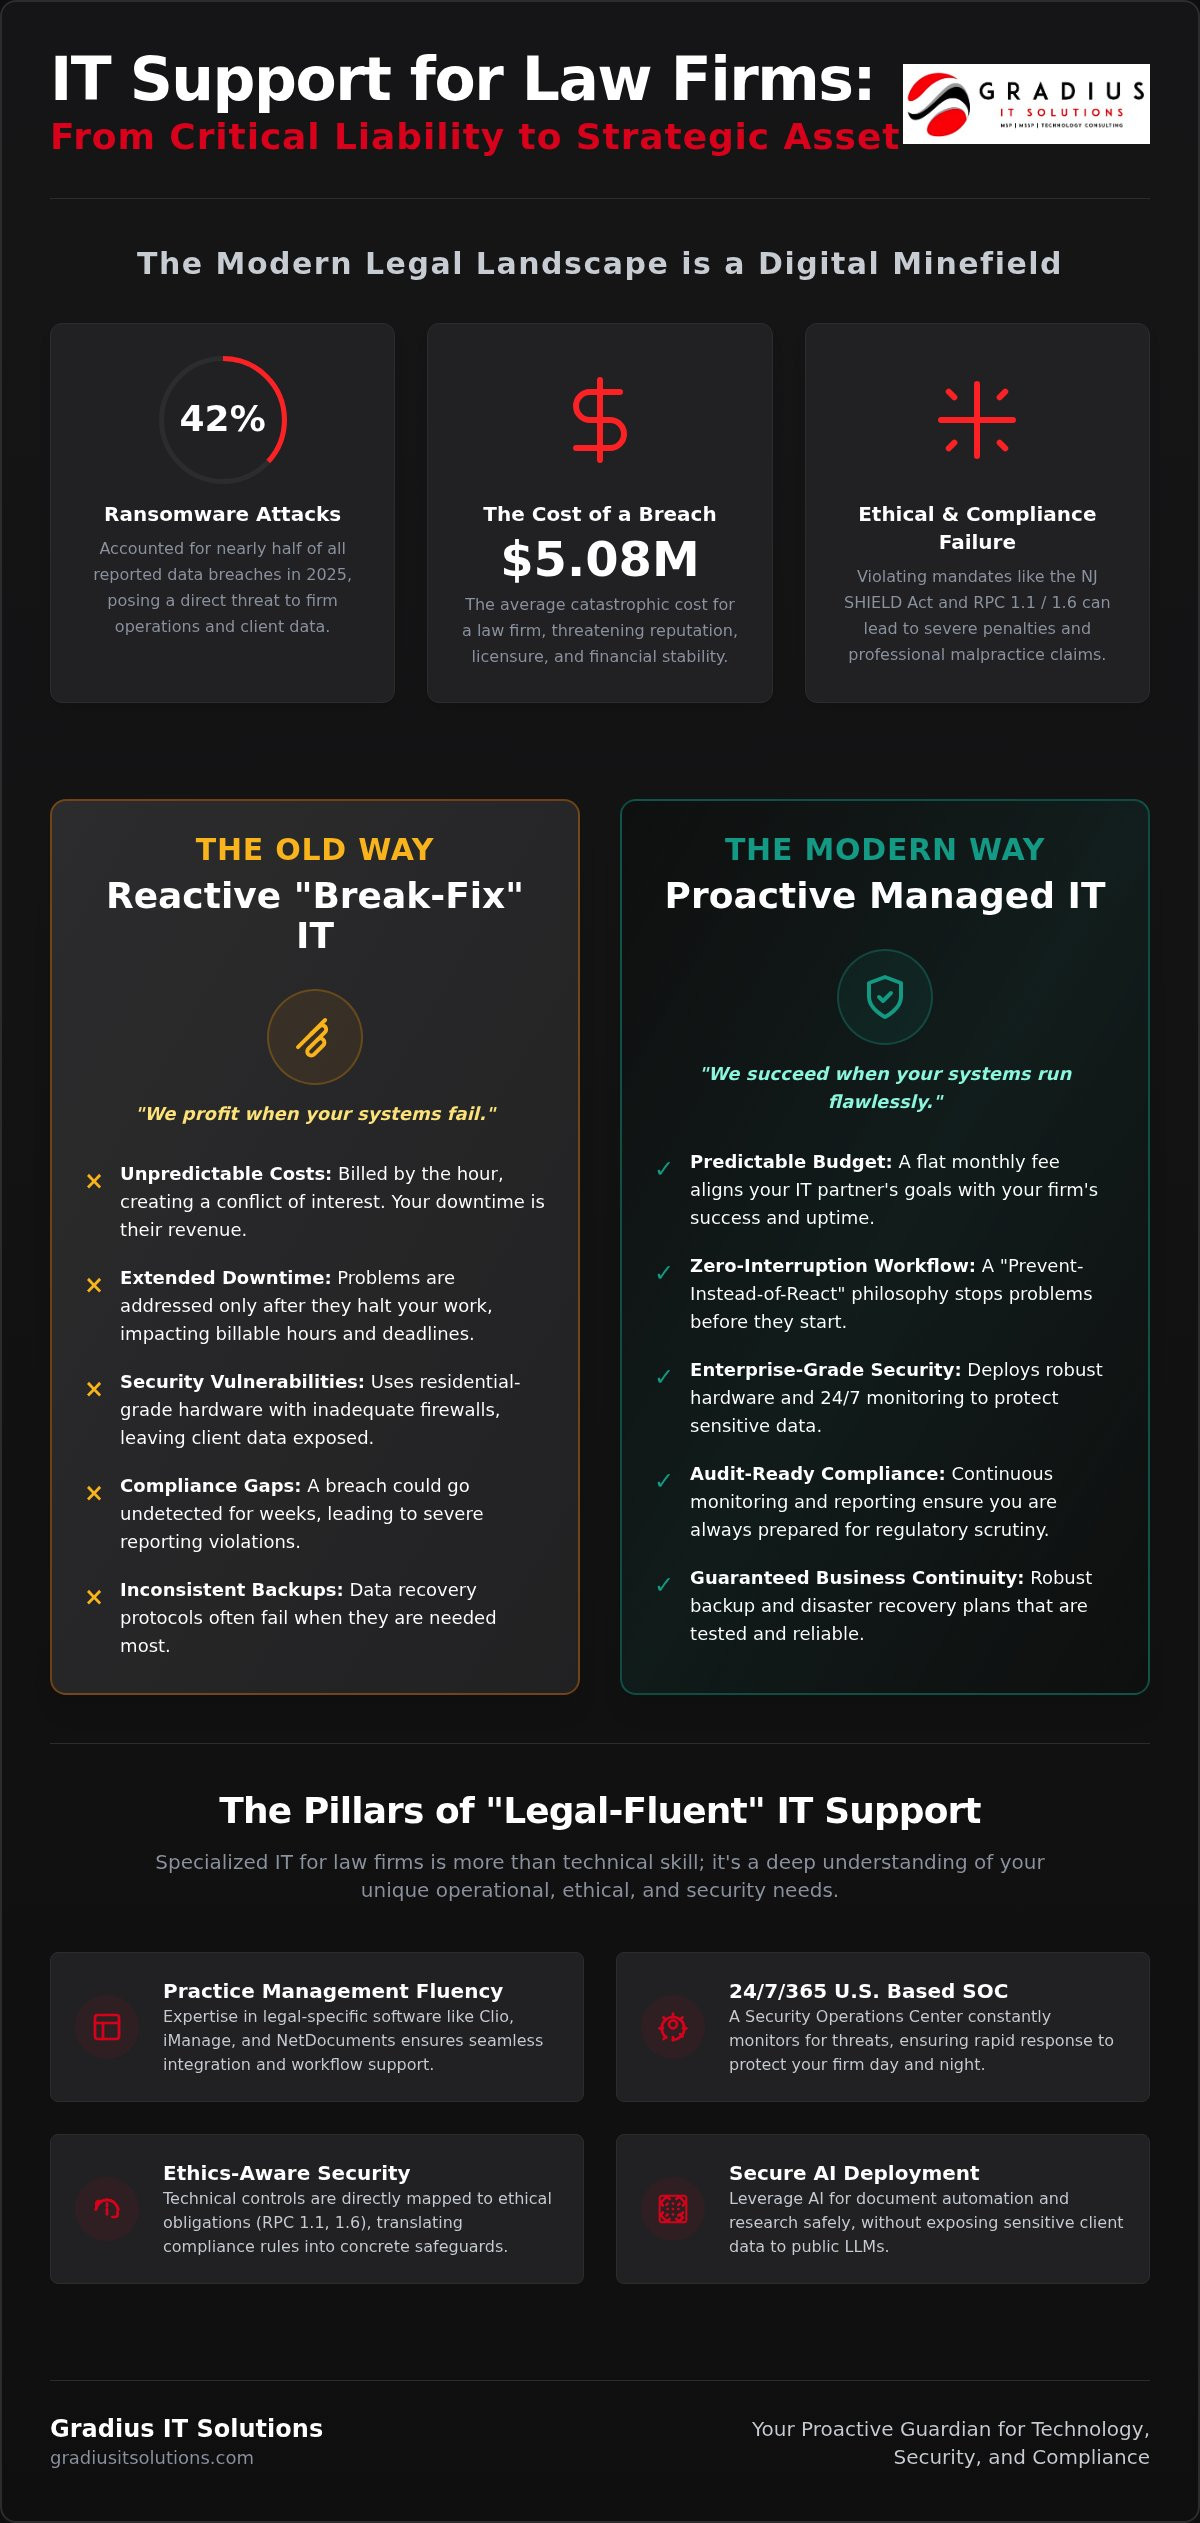
In 2025, ransomware attacks accounted for 42% of all data breaches reported to cybersecurity authorities. For a law firm, that isn’t just a technical failure. It’s a $5.08 million catastrophe that threatens your license and your reputation. You’ve likely spent late nights worrying if your current IT setup could actually withstand a targeted breach or if a critical filing deadline might be missed due to a sudden system crash. It’s a heavy burden to carry while you’re trying to win cases and manage a practice.
This guide shows you how to transform your technology from a source of anxiety into a high-performance asset. You’ll discover how to achieve zero-interruption workflows while meeting the strict demands of industry-specific compliance standards and evolving data privacy acts, including anticipated 2026 amendments. We’re exploring the intersection of ethical obligations, strategic it support for law firms nj, and the secure deployment of AI to drive your firm’s efficiency without compromising client confidentiality. It’s time to move beyond basic troubleshooting. You need a proactive guardian that keeps you three steps ahead of both hackers and regulators.
Key Takeaways
- Learn how to align your technical safeguards with the NJ SHIELD Act and RPC 1.1 to ensure your firm remains audit-ready and ethically compliant.
- Discover why specialized it support for law firms nj must move beyond the “break-fix” model to provide zero-interruption workflows during critical trial preparation.
- Identify how to leverage Secure AI for document automation and research without exposing sensitive client data to public LLMs.
- Get a practical framework for evaluating managed service providers based on legal-specific security requirements and U.S. based SOC capabilities.
- Understand the “Prevent-Instead-React” philosophy that eliminates technical friction and protects your firm’s reputation from evolving cyber threats.
IT Support for Law Firms in NJ: Beyond the Helpdesk
Law firms operate on a different clock. When a filing deadline is at 11:59 PM, “business hours” helpdesk support is useless. Specialized it support for law firms nj isn’t just a technical commodity; it’s a strategic alignment of high-availability infrastructure with strict regulatory mandates. It ensures that your digital environment is as robust as your legal arguments. You need a system that stays up when the pressure is on, not one that requires a phone call every time a printer stalls.
Modern Legal technology has moved beyond simple word processing. It now encompasses complex cloud ecosystems, encrypted communication channels, and AI-driven research tools. Relying on a generalist provider who doesn’t understand the nuances of legal ethics is a risk your firm can’t afford. You need a partner who views every server and software update through the lens of professional responsibility and client confidentiality.
To better understand how specialized technology management impacts your practice, watch this helpful overview:
Most firms start with a “break-fix” model. Something stops working, you call a technician, and they bill you by the hour to fix it. This creates a fundamental conflict of interest: your IT provider profits from your downtime. In high-stakes litigation, this model is a liability. You need a Single Accountable Partner who manages IT, security, and compliance under one roof. This “Prevent-Instead-React” philosophy shifts the focus from fixing problems to preventing them entirely. It positions your IT team as a proactive guardian, already three steps ahead of potential failures.
The High Cost of Reactive IT in Legal Practices
One hour of downtime isn’t just an inconvenience. It’s a direct hit to your billable targets. If a 10-person firm loses access to their document management system for sixty minutes, the lost revenue can easily reach thousands of dollars. Beyond the immediate financial loss, reactive IT introduces several hidden risks:
- Security Vulnerabilities: Residential-grade hardware lacks the encryption and firewall capabilities required to protect sensitive client data.
- Compliance Gaps: Without 24/7 monitoring, a breach could go undetected for weeks, violating NJ SHIELD Act reporting requirements.
- Data Loss: Inconsistent backup protocols often fail during the very emergencies they were designed to mitigate.
Proactive management ensures your hardware is enterprise-ready and monitored by a U.S. based SOC. It’s the difference between a minor glitch and a firm-ending security event.
Legal-Fluent Support: Understanding Your Workflow
Your IT team must speak your language. They shouldn’t just know how to reset a password; they should understand how Clio, iManage, or NetDocuments integrate with your daily operations. During the “crunch time” of trial prep, every second counts. You need rapid response times from technicians who understand why a failed discovery upload is an emergency. Securing dedicated it support for law firms nj ensures your technology supports your workflow instead of obstructing it. Choosing a partner with specialized experience in Managed IT Services for Law Firms ensures your firm stays operational under pressure while maintaining a bulletproof security posture.
Ethics-Aware Security: Meeting NJ SHIELD and RPC 1.6 Requirements
Legal ethics and technology are now inseparable. Rule of Professional Conduct (RPC) 1.6 demands strict confidentiality, but RPC 1.1 goes further by requiring technical competence. If you don’t fully understand the security risks of your cloud storage or document sharing, you’re flirting with malpractice. Specialized it support for law firms nj bridges this gap by mapping technical controls directly to your ethical obligations. It transforms abstract rules into concrete defenses.
The NJ SHIELD Act isn’t a suggestion. It mandates specific safeguards for “Private Information,” including encryption, Multi-Factor Authentication (MFA), and regular risk assessments. For firms with 5 to 100 employees, keeping up with these evolving requirements is exhausting. This is why high-performing practices are moving to Compliance as a Service (CaaS). This model provides a continuous, audit-ready paper trail that proves you’ve met your “reasonable care” standard. While NIST’s Small Business Cybersecurity Corner provides the framework, CaaS provides the daily execution and accountability you need.
Implementing Zero Trust in a Legal Environment
The old “castle and moat” security model is dead. Zero Trust is the modern standard for legal data integrity. It operates on a simple principle: never trust, always verify. Every user, device, and connection must be authenticated before accessing sensitive client case files. Implementing robust identity management and MFA isn’t just about stopping hackers. It’s about ensuring that a single compromised password doesn’t lead to a firm-wide breach. By verifying every access request, you protect the core of your practice.
Data Breach Prevention and the NJ SHIELD Act
The NJ SHIELD Act requires three distinct types of safeguards: administrative, technical, and physical. In 2025, ransomware accounted for 42% of reported data breaches in New Jersey. Prevention requires more than just standard antivirus software. It requires comprehensive incident response planning and parallel observation modes that detect anomalies before they escalate into disasters. A proactive approach to Compliance and Security for Law Firms ensures that if an attack is attempted, your firm is prepared to respond instantly. If you’re unsure if your current setup meets the June 30, 2026, NJ Data Privacy Act amendments, a quick security posture review can provide the clarity you need to stay protected.
Evaluating Managed IT Services for Legal Practices: A Comparison Framework
Selecting a technology partner is a fiduciary decision. For partners and office managers, the choice isn’t just about who can fix a laptop. It’s about who understands the professional liability tied to every byte of data. Generic providers often focus on simple uptime. While uptime is necessary, specialized it support for law firms nj focuses on the intersection of performance and professional ethics. You need a partner who views your infrastructure as a secure vault, not just a utility.
When interviewing a potential MSP, use this specific checklist to separate generalists from legal specialists:
- Data Sovereignty: Is your Security Operations Center (SOC) exclusively U.S. based?
- Software Fluency: Do you have certified experience with Clio, iManage, or NetDocuments?
- Compliance Documentation: Can you provide audit-ready reports for NJ SHIELD and the NJ Data Privacy Act?
- Pricing Alignment: Do you offer a flat-fee model that incentivizes prevention over hourly billing?
A U.S. based SOC is non-negotiable for 2026. Data sovereignty matters when handling sensitive litigation. You must know exactly where your data is monitored and who has access to it. Beyond the security benefits, flat-fee pricing eliminates the conflict of interest inherent in hourly billing. It ensures your IT partner is motivated to keep your systems running perfectly, rather than profiting from your downtime.
Key Performance Indicators (KPIs) for Legal IT
Response time is a vanity metric. If a technician answers the phone in five minutes but takes five hours to fix the problem, your billable targets still suffer. You should prioritize resolution time. A high-performance specialist focuses on how quickly you are back to work. Assuming your data is safe just because a backup is running is a dangerous mistake. Without monthly restore tests, a backup is just a file that might fail when you need it most. Your vCIO should provide regular verification that your disaster recovery plan actually works under pressure.
Managed Security vs. Basic IT Support
Standard IT support is reactive. It handles patches, passwords, and printers. In contrast, a Managed Security Service Provider (MSSP) approach provides the layered defense required by modern ethics rules. Before committing to a new contract, perform a thorough IT Risk Assessment to identify your current vulnerabilities. Law firms that also serve financial clients or operate under securities regulations may benefit from reviewing the FINRA IT compliance support framework to understand how overlapping regulatory standards can be addressed within a single managed security strategy.
| Feature | Basic IT Support | Legal-Specific Managed IT |
|---|---|---|
| Security Focus | Antivirus & Firewall | EDR, SIEM, & 24/7 SOC |
| Compliance | Best Effort | Audit-Ready Documentation |
| Strategic Planning | None | vCIO Business Alignment |
Layered security is the only way to meet the “technical competence” requirement of RPC 1.1. By combining email security, endpoint protection, and network monitoring, you create a resilient environment that protects your firm’s reputation and bottom line. Reliable it support for law firms nj doesn’t just keep the lights on; it ensures you stay in business. For firms that advocate for those who served, you can learn more about Military Veteran Solutions, LLC to see how they help veterans navigate the complexities of obtaining their entitled benefits.
Optimizing Legal Workflows with Secure AI and Practice Management
AI has reached a tipping point for the legal industry. It’s no longer a futuristic concept; it’s a practical tool for reclaiming billable hours. High-performance it support for law firms nj now includes the strategic deployment of automation to handle high-volume tasks. AI excels at summarizing depositions, drafting initial contracts, and reconciling complex billing entries. These tools don’t replace attorneys. They empower them by stripping away the administrative friction that slows down case progression.
The greatest risk to your firm’s reputation is “Shadow AI.” This occurs when staff use public, unsecured Large Language Models (LLMs) to process sensitive client data. Public tools often store your inputs to train their models, which can lead to catastrophic data leaks and ethics violations. You need Secure AI agents that operate within a “walled garden” environment. This ensures your data stays under your control while still providing the speed and efficiency of modern automation.
Secure AI Adoption for Small and Mid-Sized Firms
Implementing a tool like Microsoft 365 Copilot requires more than just a license. It requires a deep understanding of data governance. You must configure Microsoft Purview to enforce strict compliance settings. This ensures the AI only accesses information the specific user is authorized to see. Beyond research, you can deploy secure chatbots to handle client intake and scheduling. This reduces the burden on your front-office staff and provides a better experience for your clients. By following a structured roadmap for Secure AI and Automation Services, you can modernize your practice without compromising your security posture.
Deploy Secure AI and Automation Services Today
Cloud Management and Microsoft 365 Hardening
Moving from aging on-premise servers to a secure cloud environment is the foundation of a resilient practice. However, a “set it and forget it” approach to the cloud is a liability. You need hardened Microsoft 365 policies that include robust email archiving and Data Loss Prevention (DLP). These policies act as a safety net, preventing sensitive case details from being shared accidentally with unauthorized parties. Specialized it support for law firms nj ensures that your cloud collaboration tools are as secure as they are productive. This proactive hardening protects your firm during the discovery process and ensures you always meet your duty of technical competence.
Strategic Partnership: Why NJ Law Firms Choose Gradius IT Solutions
Choosing an IT partner isn’t just about technical proficiency. It’s about finding a champion for your firm’s success. Most providers wait for things to break. At Gradius, we reject that mediocrity. Our “Prevent-Instead-React” philosophy ensures your technology works for you, not against you. We position ourselves as a proactive guardian, anticipating obstacles before they disrupt your billable hours. This is the level of it support for law firms nj that high-performing practices require to stay competitive in 2026.
We provide a 24/7 U.S.-based Security Operations Center (SOC) and Network Operations Center (NOC). This isn’t a vague promise of “monitoring.” It’s a dedicated team of experts watching your environment every second of every day. Because our SOC is entirely domestic, your data stays within U.S. jurisdiction, fulfilling the highest standards of data sovereignty. We combine this protective force with a “No Hidden Fees” flat-fee pricing model. You’ll never see a surprise bill for an “emergency” fix. Our success is tied directly to your stability.
The Gradius vCIO: Your Strategic Technology Partner
Technology should be a growth driver, not a line-item expense. Your dedicated Virtual Chief Information Officer (vCIO) provides high-level strategic planning to align your IT spend with your long-term goals. We don’t just manage servers; we manage your technology roadmap. This includes comprehensive vendor management. We handle the phone companies, internet providers, and software vendors so your staff can focus on the law. Specialized it support for law firms nj involves constant refinement of your security posture. If you already have an IT manager, we act as a staff augmentation force, providing the specialized cybersecurity and compliance depth they need to succeed.
Getting Started: The IT and Cybersecurity Assessment
We believe in accountability and transparency. That’s why we offer a free, no-obligation 30-minute IT and Cybersecurity Assessment. During this consultation, we’ll look at your current infrastructure, security protocols, and compliance posture. We won’t waste your time with industry jargon. You’ll get straight talk about your risks and opportunities. Within one week of our meeting, you’ll receive a clear, written compliance gap analysis. This document highlights exactly where your firm stands relative to the NJ SHIELD Act and modern security standards. It’s the first step toward a zero-interruption workflow and total peace of mind.
Securing Your Firm’s Future in a Digital-First Legal Landscape
The legal landscape in 2026 demands more than just basic troubleshooting. It requires a strategic alignment of technical safeguards with your ethical obligations under the NJ SHIELD Act and RPC 1.1. By moving beyond the reactive “break-fix” model, your practice can achieve zero-interruption workflows and leverage Secure AI to maximize billable efficiency. Reliability is no longer an option. It is the foundation of your professional reputation.
Gradius IT Solutions stands as your proactive guardian. We combine a U.S. based 24/7 SOC with specialized Compliance as a Service to ensure your firm is always audit-ready. Our Prevent-Instead-React methodology eliminates the technical friction that stalls trial prep and filing deadlines. Professional it support for law firms nj ensures your technology remains a high-performance asset rather than a source of anxiety. It is time to stop worrying about downtime and start focusing on winning cases.
Your firm deserves a partner who is already three steps ahead of the next threat. Take the first step toward a more resilient, efficient, and compliant practice today.
Frequently Asked Questions
What is the NJ SHIELD Act, and does it apply to my law firm?
The NJ SHIELD Act applies to any business that collects the “private information” of New Jersey residents. It mandates that your firm implements administrative, technical, and physical safeguards to protect this data. Failure to comply can result in significant civil penalties. We help you meet these requirements by deploying encrypted storage, multi-factor authentication, and documented security policies that satisfy regulatory audits.
How does managed IT support improve billable hours?
Reliable it support for law firms nj protects your billable targets by preventing system crashes before they happen. When your document management and billing systems are always available, your team stays productive. We also use secure automation to handle non-billable administrative tasks. This allows your attorneys to focus entirely on casework instead of fighting with slow software or disconnected servers.
Is a U.S.-based SOC really necessary for legal cybersecurity?
Data sovereignty is a critical component of legal ethics and client confidentiality. A U.S.-based SOC ensures that the professionals monitoring your network are subject to domestic privacy laws and security standards. This eliminates the risks associated with offshore data access. It ensures your firm meets the highest standards of security while keeping sensitive litigation data within U.S. legal jurisdiction.
Can you support our specific practice management software like Clio or iManage?
We provide expert support for all major legal platforms, including Clio, iManage, and NetDocuments. Our team understands how these tools integrate with your broader Microsoft 365 environment. We don’t just fix software errors; we optimize your entire digital workflow. This ensures these platforms perform at peak efficiency when you are facing critical trial deadlines or high-volume discovery.
What is the difference between an MSP and an MSSP for law firms?
A Managed Service Provider (MSP) handles your daily technical needs like helpdesk and patches. A Managed Security Service Provider (MSSP) focuses on advanced threat detection and 24/7 monitoring. Law firms need a partner that provides both. You need your systems to be operational and defended against sophisticated cyberattacks, which is why we integrate security into every managed service we offer.
How do you handle cybersecurity for remote or hybrid attorneys?
We secure remote workflows using Zero Trust principles. This means every connection is verified through multi-factor authentication and endpoint protection. Whether your attorneys are in the office, at home, or in the courtroom, their access to sensitive case files remains encrypted and strictly controlled. This prevents unauthorized data leaks while allowing your team to work from any location securely.
What happens if we have a critical IT issue during a trial?
Our 24/7 NOC and helpdesk provide immediate assistance for critical issues. While our “Prevent-Instead-React” methodology stops most problems before they start, we prioritize trial-related emergencies. You get rapid resolution from technicians who understand the high stakes of legal deadlines. We ensure your technology stays out of the way so you can focus on your arguments and your clients.
Do you provide audit support for our malpractice insurance renewals?
We provide full audit support for malpractice insurance and regulatory reviews. Insurers now require detailed proof of your security posture, including MFA implementation and incident response plans. We deliver the necessary documentation and compliance reporting to prove you meet these standards. This helps you secure favorable insurance terms and ensures your firm remains audit-ready and fully protected.
Article by
Robert Joyce
**Robert Joyce** is the Founder, CEO, and Chief Technology Officer of Gradius IT Solutions, a security first provider of Managed IT Services, Cybersecurity, Cloud, Compliance, and Secure AI solutions serving businesses throughout New Jersey, New York, Connecticut, and across the United States.
With more than 28 years of IT experience, including 23 years supporting hedge funds, global banks, and wealth management firms, Robert has built a career designing and managing secure, resilient, and highly available technology environments where uptime, cybersecurity, and business continuity are essential.
His expertise includes Microsoft 365, cloud computing, cybersecurity, networking, infrastructure, disaster recovery, compliance, virtualization, and strategic IT leadership. Following the events of September 11, Robert helped rebuild critical technology infrastructure for Merrill Lynch, an experience that reinforced the importance of resilience, planning, and operational excellence.
Robert founded Gradius IT Solutions to bring enterprise level technology and security services to small and midsized businesses at a predictable monthly cost. Today, the company delivers fully managed and co managed IT services, cybersecurity, Microsoft 365, cloud solutions, compliance consulting, Secure AI consulting, technology projects, and vCIO services. Through a U.S. based 24/7 Help Desk and a nationwide network of trusted technology partners, Gradius supports organizations across the country with responsive, security focused technology solutions.
Robert partners with business owners and executive leaders to align technology with business goals, reduce risk, strengthen cybersecurity, improve productivity, and create long term IT strategies that support growth. His mission is simple: provide every client with enterprise class technology, exceptional service, and a trusted advisor they can rely on as their business evolves.
Disclaimer
## Disclaimer
The information provided in this article is for general informational and educational purposes only and should not be considered professional IT, cybersecurity, legal, regulatory, or compliance advice. While Gradius IT Solutions strives to provide accurate and up to date information, technology, security threats, and regulatory requirements change frequently, and we cannot guarantee that all information will remain current or applicable to your specific situation.
Every organization has unique technology, security, compliance, and business requirements. Before implementing any recommendations discussed in this article, you should evaluate their suitability for your environment or consult with a qualified technology professional.
Gradius IT Solutions makes no warranties, express or implied, regarding the completeness, accuracy, reliability, or results obtained from the use of this information. Any actions you take based on this content are at your own risk. Gradius IT Solutions shall not be liable for any direct, indirect, incidental, or consequential damages arising from the use of, or reliance upon, the information contained in this article.
References to third party products, services, or vendors are provided for informational purposes only and do not constitute an endorsement unless explicitly stated.
If you would like guidance tailored to your organization, contact Gradius IT Solutions to schedule a consultation with one of our technology experts.