Last Updated: November 7, 2026
Quick Summary
To build a compliance management system, start by writing down every obligation that applies to you and ranking each by likelihood and impact. Then name one accountable owner, map controls to a single framework, and keep evidence records. Run spreadsheets for the first two quarters before buying software.
- Six core components: obligations, policies, roles, risk assessment, monitoring, and documentation.
- Pick one framework as your spine, such as NIST CSF or CIS Controls, not both.
- Keep the policy set short: ten clear policies staff follow beat forty nobody reads.
- A 22-person accounting firm ran its program with one owner at roughly four hours a week.
- Track four KPIs from day one, including training completion and time to remediate.
Table of Contents
- What Is a Compliance Management System and Why Does It Matter?
- Step 1: Assess Your Compliance Obligations and Risks
- Step 2: Build Your Compliance Framework and Policies
- A Real-World Compliance Management System Example for Small Teams
- Your Compliance Management System Checklist for Launch
- Compliance Management System Template: What to Include
- Choosing Compliance Management System Software vs. Spreadsheets
- How to Measure Program Effectiveness and Avoid Common Mistakes
- Frequently Asked Questions
What Is a Compliance Management System and Why Does It Matter?
A compliance management system is the set of policies, controls, people, and records a business uses to meet its legal and industry obligations and to prove it did so.
That distinction matters more than most beginners expect. A small firm can pass one audit with a scramble. It cannot pass the next three without a system.
The rules were never the hard part. Keeping track of them was.
The Core Components Every CMS Needs
Six parts do most of the work:
- Obligations: the laws, regulations, and industry standards that apply to you
- Policies and procedures: written rules that say what staff must do
- Roles and accountability: a named owner for each control
Miss any one and the program develops a gap. Most often, it is accountability.
Step 1: Assess Your Compliance Obligations and Risks
Start by writing down every rule that touches your business. Do not guess. Pull the actual text from the source.
Common sources for a small organization include:
- Federal and state privacy and breach-notification laws
- Sector rules such as HIPAA for healthcare or PCI DSS for card payments
- Contract terms from clients, insurers, and vendors
Then rank each obligation by two factors: how likely a failure is, and how much damage it would cause. That ranking is your risk assessment, and it decides what you fix first.
A practical guide to building a proactive compliance strategy helps smaller teams sort obligations by size and risk. If you need a deeper method for quantifying and documenting IT risk, that framework walks through scoring and evidence.
Watch out: beginners copy a checklist from the internet and treat it as their obligation list. It rarely matches their contracts or their state rules.
Step 2: Build Your Compliance Framework and Policies
A framework is a shared vocabulary. Without one, every new obligation becomes a fresh argument about what to do. With one, you map each requirement to a known control and reuse the work.
Two frameworks fit small organizations well:
- NIST Cybersecurity Framework (CSF): organized around Identify, Protect, Detect, Respond, and Recover (The CSF 1.1 Five Functions | NIST). Good for explaining the program to leadership and insurers.
- CIS Critical Security Controls: a prioritized list of safeguards with implementation groups by organization size (CIS Critical Security Controls Implementation Groups). Good for deciding what to do first.
You do not need both. Pick one as your spine, then map other obligations to it. A HIPAA safeguard, a client questionnaire item, and a cyber insurance control can all point to the same underlying control, for example, multi-factor authentication or quarterly access reviews.
Map Controls Before You Write Policies
Build a simple control map before drafting a single policy. For each obligation, record:
- The requirement in plain language
- The control that satisfies it
- The system or process where the control lives
- The evidence that proves it works
- The named owner
This map is what stops duplicated work. When a new client questionnaire arrives, you check the map instead of starting over.
Write Policies People Will Actually Follow
Each policy needs four things: the rule, who it applies to, who owns it, and how often it is reviewed. Keep the set short, ten clear policies staff follow beat forty nobody reads. Typical starters for a small business include acceptable use, access control, incident response, backup and recovery, vendor management, and data retention.
Pair every policy with a procedure that says how the rule is carried out day to day. A policy says “access is reviewed quarterly.” A procedure says who pulls the user list, who approves changes, and where the sign-off is saved.
Assign Roles and Accountability
This is where most beginner programs stall. Name one accountable owner, often an operations manager, practice manager, or IT director, with real authority to enforce policy. Around that person, define a small set of roles even if one person wears several hats:
- Program owner: owns the control map and the review calendar
- Control owners: the person responsible for each control (for example, the office manager owns access reviews)
- Leadership sponsor: approves policy and resolves conflicts
Write the roles down. An unwritten role is a role nobody performs.
Train and Communicate
Training is not a one-time event. Assign role-based training, general security awareness for everyone, deeper training for anyone handling regulated data or admin accounts, and track completion.
Watch out: beginners publish policies to a shared drive and assume staff have read them.
A framework gives you structure so you are not inventing categories from scratch. Our guide to implementing the NIST Cybersecurity Framework shows how to map existing controls to a framework without starting over.
A Real-World Compliance Management System Example for Small Teams
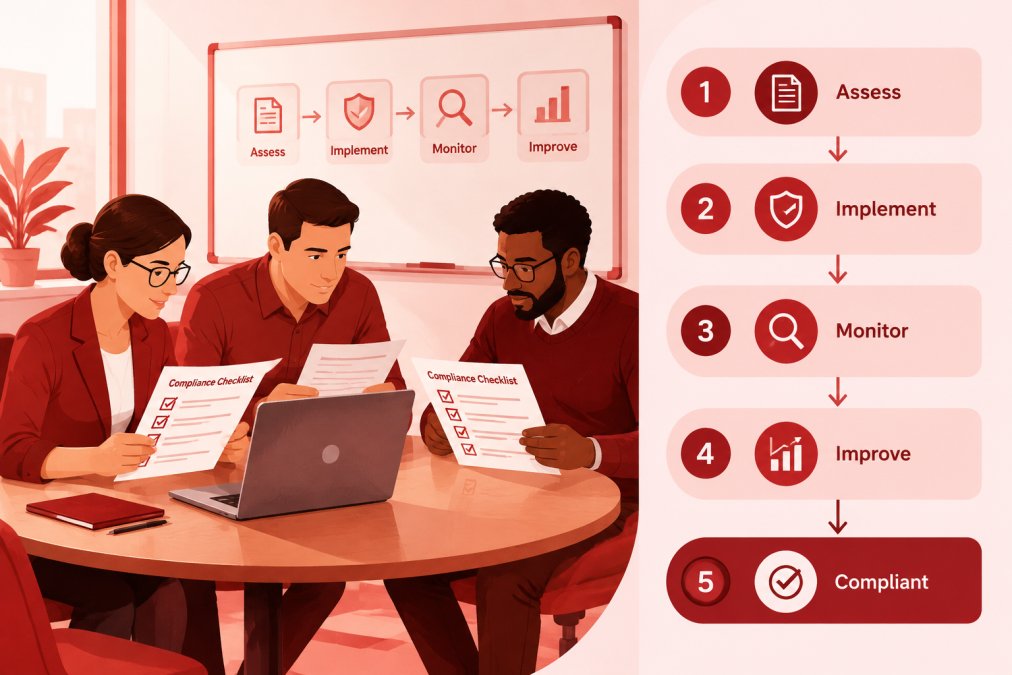
Picture a 22-person accounting firm that must satisfy client security questionnaires and its cyber insurance renewal.
Here is what worked:
- One named compliance owner, roughly four hours a week
- A single spreadsheet listing every obligation, owner, and due date
- Quarterly access reviews with screenshots saved to a shared folder
No new software. No consultant on retainer. The firm built the habit first, then bought tools once the manual process hurt.
That order matters.
Your Compliance Management System Checklist for Launch
Use this to confirm the basics are in place before you call the program live:
- Obligation list written and ranked by risk
- One accountable owner named in writing
- Core policies published and acknowledged by staff
If three or more boxes are empty, fix those before adding anything new.
Compliance Management System Template: What to Include
A working template has five tabs or sections. Keep them plain.
| Section | What Goes In | Review Cycle |
|---|---|---|
| Obligation register | Rule, source, owner, due date | Quarterly |
| Risk register | Risk, likelihood, impact, treatment | Quarterly |
| Policy index | Policy name, owner, last review | Annual |
| Evidence log | Control, proof, date collected | Monthly |
| Training record | Staff member, course, completion date | Monthly |
The template is the easy part. Filling it in honestly is where programs succeed or stall.
Choosing Compliance Management System Software vs. Spreadsheets
Spreadsheets win early. They cost nothing, they are flexible, and they force you to understand your own data before a vendor shapes it for you.
Software wins once you pass a few thresholds:
- More than one person updates the records
- Evidence collection eats hours each month
- You face multiple frameworks at once
A middle path exists. Comparing continuous compliance monitoring services and reporting tools helps you see where automation stops and human ownership begins.
Our advice: run spreadsheets for the first two quarters. Buy software when the manual process genuinely breaks, not before.
How to Measure Program Effectiveness and Avoid Common Mistakes
A program you cannot measure is a program you cannot defend at renewal time. Pick a small set of numbers, define them precisely, and review them on a fixed cadence.
Four KPIs Worth Tracking From Day One
- Training completion rate: staff current on required training divided by total staff. Target: 100% within 30 days of assignment.
- Open findings: issues identified and not yet closed. Track the count and the age of each finding.
- Time to remediate: average days from finding to verified fix. Track by severity so a single critical issue does not hide behind easy fixes.
Review these monthly with the program owner and quarterly with leadership. A rising open-findings count alongside a falling remediation time is healthy, it means you are finding more and fixing faster. A falling count with rising remediation time usually means people stopped looking.
A Phased 90-Day Plan for Beginners
Here is a realistic order for a small organization with limited staff:
Days 1-30, Establish the baseline
- Name the program owner and leadership sponsor in writing
- Build the obligation register from actual contract, insurance, and regulatory text
- Rank obligations by likelihood and impact
Days 31-60, Build the core
- Draft the first six policies and pair each with a procedure
- Map controls to the chosen framework
- Assign control owners
Days 61-90, Prove it works
- Run the first quarterly access review and save the evidence
- Test the incident response plan once as a tabletop exercise
- Hold the first monthly KPI review
This order matters. Building controls before you know your obligations wastes effort, and buying software before the manual process exists just documents the mess faster.
Prioritize When Budget and Staff Are Limited
Beginners often try to fix everything at once. Use three tiers instead:
- Mandatory now: obligations tied to law, contract, or insurance renewal. These get done first regardless of cost.
- High-leverage next: controls that satisfy multiple obligations at once, such as MFA, access reviews, and backup testing.
- Improvement later: maturity items that reduce risk but are not yet required.
When two mandatory items compete for the same week, pick the one with the nearest external deadline.
Manage Overlapping Regulations and Track Changes
Most small firms face more than one rule set at once. Use the control map from Step 2 to satisfy several requirements with one control and one evidence record. Then assign one person to watch for regulatory changes, a quarterly check of the sources in your obligation register is enough for most small businesses. When a rule changes, update the register, the affected policy, and the evidence log in the same pass.
Common Mistakes to Avoid
- Assigning compliance to someone with no authority to enforce it
- Writing policies nobody trains on or acknowledges
- Collecting evidence once and never refreshing it
Ongoing monitoring and audit-ready evidence are what separate a real program from a yearly panic. Seeing how continuous monitoring works in practice makes that difference concrete.
If building and running that program in-house is more than your team can take on, Gradius can help you talk through what ongoing monitoring and evidence work would involve for your environment.
Frequently Asked Questions
What are the five C’s of compliance?
The five C’s are a common framework: Commitment from leadership, Controls to enforce policies, Communication of expectations, Competence through training, and Continuous improvement. For a beginner building a compliance management system, these map to practical steps: get owner buy-in, write policies, train staff, assign responsibilities, and schedule reviews. Each C reinforces the others, so a gap in one weakens the whole program. Use the five C’s as a simple self-check when you review your system.
How do you start a compliance management system?
Start by listing the laws, regulations, and industry standards that apply to your business, such as HIPAA for healthcare or PCI DSS for card payments. Then assign a compliance lead, draft a code of conduct and key policies, and set up a training schedule. A compliance management system checklist helps you track these first steps. Begin with the highest-risk obligations and expand over 90 to 180 days. Document every decision so you can show your work during an audit or cyber insurance review.
What should a compliance management system template include?
A useful compliance management system template includes sections for scope, regulatory requirements, risk assessment, policies and procedures, roles and responsibilities, training records, monitoring and testing schedule, incident response, and corrective action log. Add a document control page with version numbers and review dates. Templates save time but must be adapted to your actual obligations. Review the template with legal counsel or a compliance advisor before adopting it, especially for regulated industries like healthcare or financial services.
How do you measure whether a compliance program is effective?
Track defined KPIs such as training completion rate, policy review cycle adherence, number of audit findings and time to remediation, incident response times, and third-party risk assessments completed. Review these metrics quarterly with leadership. Effectiveness also shows in fewer repeat findings and faster corrective action. A compliance management system software tool can automate tracking, but spreadsheets work for small teams. Use the data to adjust priorities, not just to report status.
